Implementing Multi-Environment Access for Claude Platform on AWS
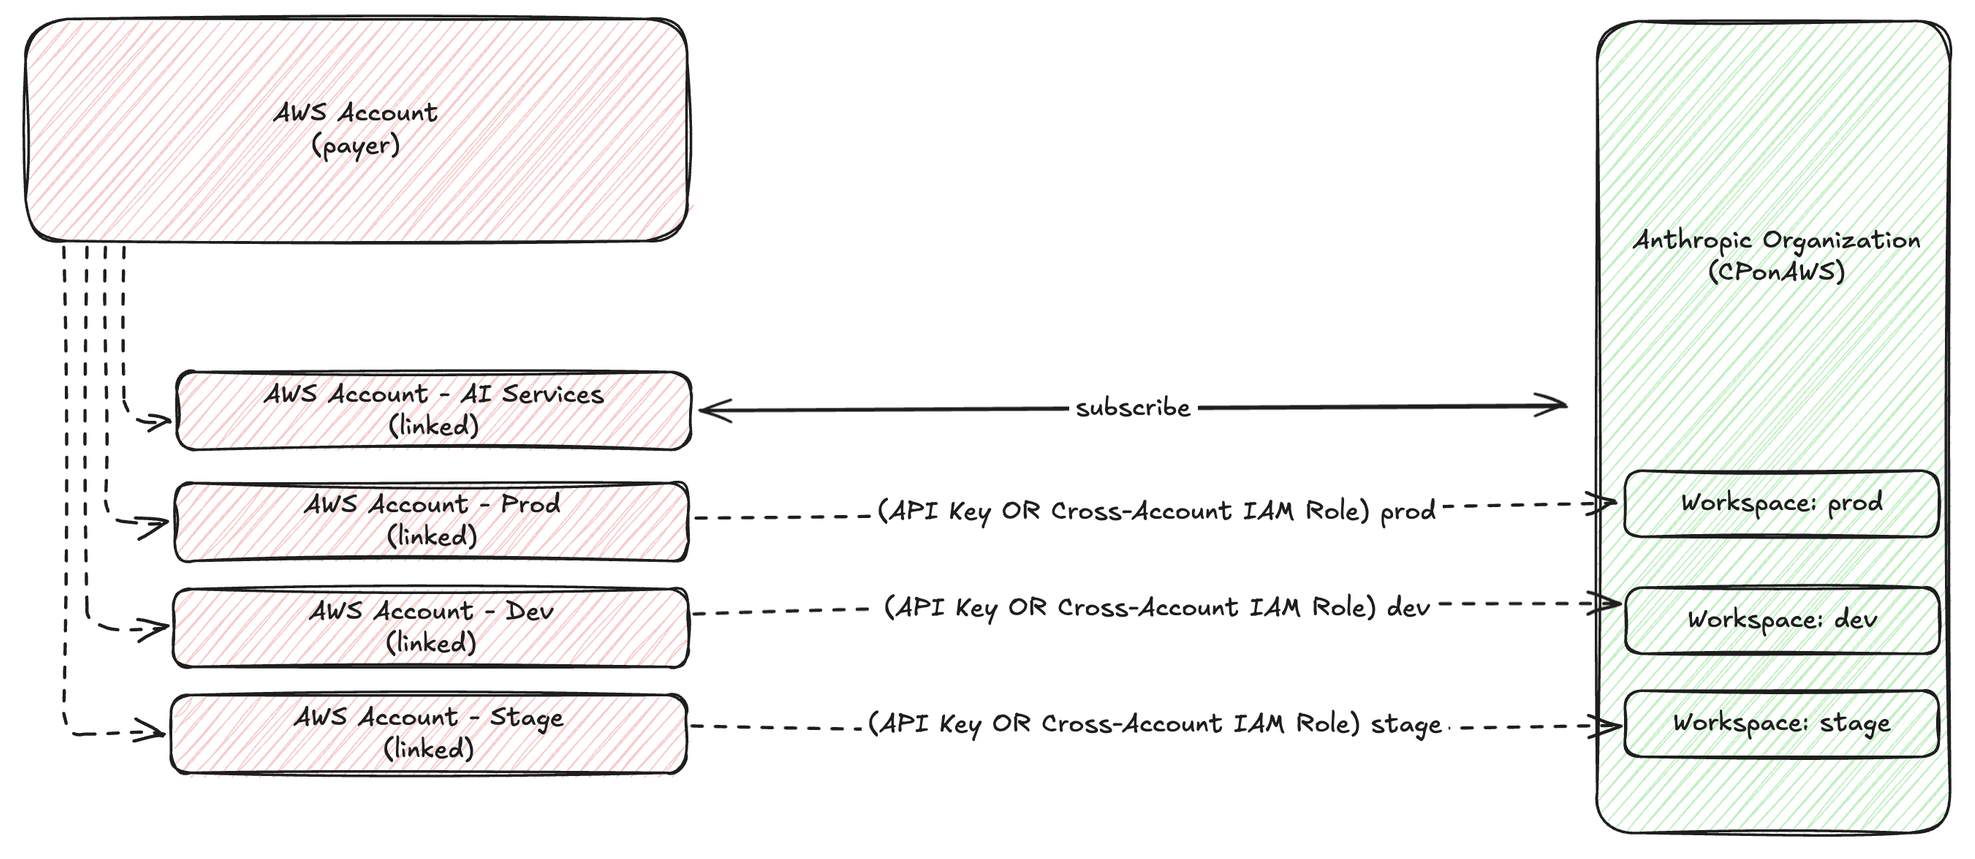
An AWS Machine Learning Blog post outlines a step-by-step implementation for accessing Claude Platform on AWS (CPonAWS) inference from three environments: production workloads on AWS, developer laptops, and external services on other cloud providers or on-premises CI/CD pipelines. According to the post, each environment has different authentication requirements but all share a single subscription with workspace-level isolation between production and development traffic.
The architecture places the CPonAWS subscription in a dedicated AI Services linked account, producing a three-account structure: a payer (management) account for billing and governance, the AI Services account that owns the subscription, workspaces, API keys, and cross-account roles, and one or more workload accounts that consume inference by assuming roles into the AI Services account.
Three access patterns are configured. For AWS workload accounts, an Amazon EKS pod in a workload account assumes a role in the AI Services account and makes SigV4-signed inference calls, with no stored API keys. The cross-account role's CreateInference permission is scoped to the production workspace ARN, so it cannot access the development workspace. For developer laptops, a long-lived API key is locked to a development workspace after detaching the default AnthropicLimitedAccess managed policy and attaching an inline policy naming the development workspace resource. For external workloads, OpenID Connect federation lets a workload outside AWS authenticate, obtain temporary AWS credentials, and generate a short-lived token.
Preparation requires an AWS Organizations organization with a payer account, an AI Services linked account, and a workload linked account, plus AWS CLI v2 with named profiles and Python 3.12 or later with the anthropic[aws], boto3, and token-generator-for-aws-external-anthropic packages. The post states workspaces are created in a specific AWS Region and API calls must target the matching Regional endpoint; the workspace Region determines the endpoint, not where inference runs. Current security settings options for inference geography are "US" and "Global routing."
Based on reporting from the original publisher. Visit the source for full context and later updates.
Publisher excerpt
Learn how to configure secure, multi-environment access to Claude Platform on AWS from a single subscription: cross-account SigV4 for AWS workloads, workspace-scoped API keys for developers, and OIDC federation for external environments, with workspace-level isolation in a dedicated AI Services account.